
Microsoft Said the Always On VPN Fix Landed October 13. It Did Not.
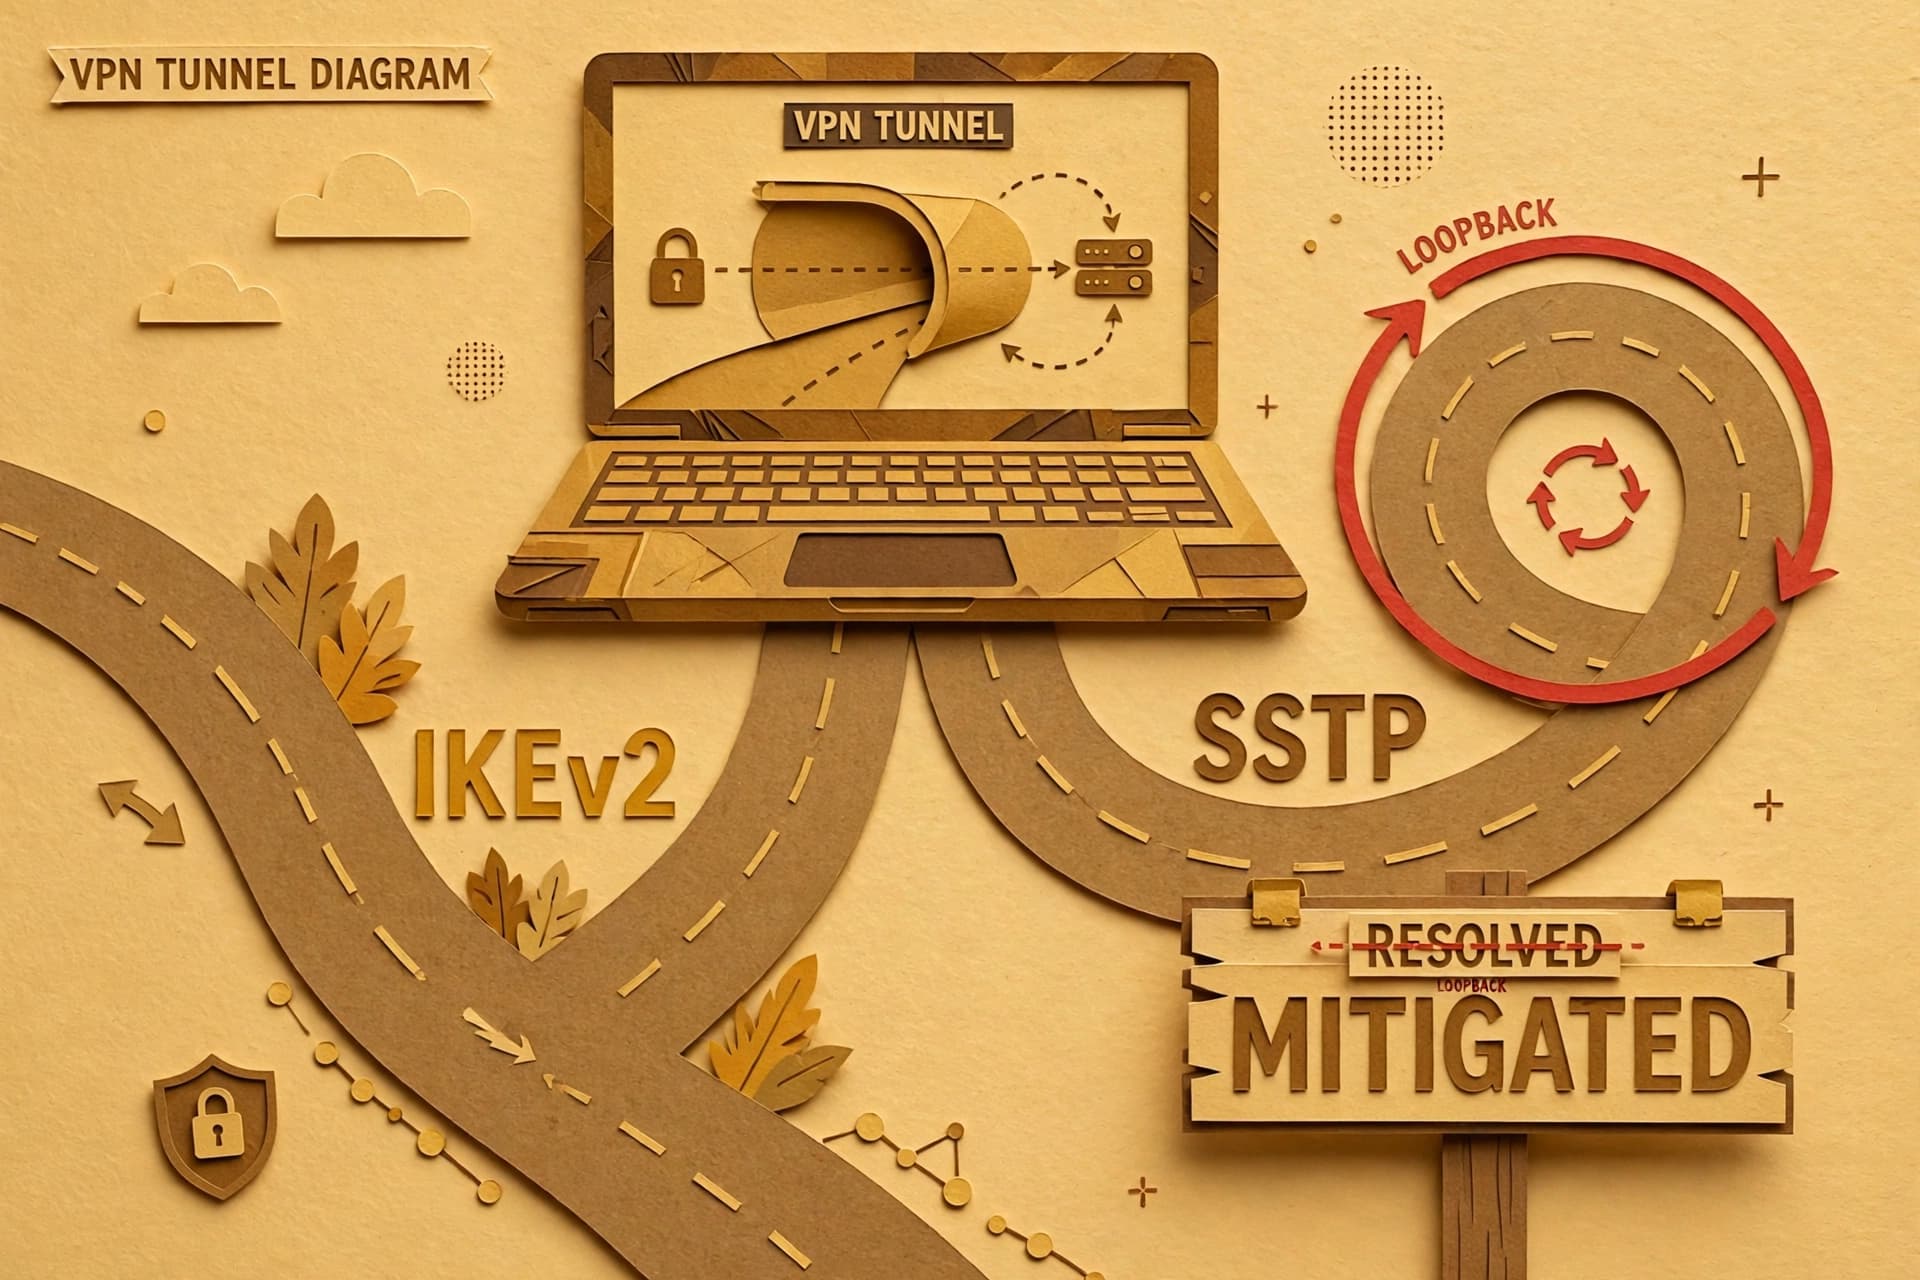
On October 20, Microsoft quietly walked back one of its own fix announcements. The Always On VPN problem that the October security update was supposed to resolve is not resolved. In Microsoft's words, quoted by The Register: "This disclosure was mistakenly updated to Resolved status on October 13, 2026. We have returned its status to Mitigated. We apologize for any inconvenience or confusion."
That one word change matters more than it looks. Resolved means you can close tickets, remove workarounds, and move on. Mitigated means the workaround is still the plan. If your team read the October 13 status, told users the VPN was fixed, and rolled the workaround back, you now own a second round of the same incident.
What actually broke
The September 2026 Windows security update broke Always On VPN connections on Windows 11, versions 24H2 through 26H2. The failure needs a specific setup to trigger. The VPN profile has to be configured to try another protocol when the first attempt fails. Microsoft's own example is automatic protocol selection with IKEv2 and SSTP.
When that first connection attempt fails, the retry logic falls over. Affected connections can sit in a Connecting state, retry over and over without succeeding, or fail with a message that sounds like a server problem: "The specified port is already in use." It is not a server problem. The client has tangled itself up after the first failed attempt.
On October 13, the October cumulative updates, KB5127648 and KB5127646, were announced as the fix, and the known issue was marked resolved. BleepingComputer reported the fix the next day, in good faith, based on what Microsoft had published. A week later, Microsoft admitted the status change was a mistake. The real fix is now planned for an update "in the coming weeks," which is a direction, not a date.
Why the wrong status is its own incident
A wrong Resolved label does practical damage in three places.
First, help desks close tickets. Users who still cannot connect get told the issue is fixed, so their report starts to look like a local problem. That burns trust and sends technicians chasing laptops instead of the fleet profile.
Second, change records close too. Plenty of teams pinned a single protocol as a temporary measure in September, with a note to restore automatic selection once Microsoft shipped the fix. October 13 looked like that day. Anyone who acted on it reintroduced the bug to machines that were working fine under the workaround.
Third, it poisons the next announcement. When the real fix does land, careful admins will not believe the status page on day one. They will pilot it, watch it, and wait. That caution is rational, and Microsoft earned it.
The workaround is still the fix you control
Microsoft's guidance has not changed since September, and it is simple: change the Always On VPN profile from automatic protocol selection to a single protocol. Use SSTP only or IKEv2 only, depending on what your gateway supports and what your environment needs.
Pick deliberately, not by coin flip:
- Choose the protocol your server side is healthiest on. If your RRAS or gateway setup is proven on IKEv2, pin IKEv2. If SSTP is the path that has always worked through your firewalls and proxies, pin SSTP.
- Push it as a profile change, not a suggestion. Update the Intune or Group Policy delivered VPN profile so every managed device gets the same setting. A fix that depends on users opening settings is not a fix.
- Pilot on a small ring first. Confirm the tunnel comes up clean after a reboot, after sleep, and after a failed first attempt. That last test is the exact scenario that triggers the bug.
- Leave automatic selection off until the real fix proves itself. When Microsoft ships the coming update, test it the same way before you restore fallback behaviour.
A short triage checklist for tickets this week
- Check the Windows version. This issue applies to Windows 11 24H2 and later. Do not spend an hour on it for a Windows 10 machine.
- Check the profile. If the device uses automatic protocol selection or protocol fallback, it is in scope. If it is already pinned to one protocol, look elsewhere.
- Ask what the user sees. Stuck on Connecting, endless retries, or "The specified port is already in use" after a failed first attempt all match the known issue.
- Apply the single protocol profile and retest from a cold start.
- Keep the ticket linked to the known issue, WI1482218, instead of closing it as resolved. The status that matters is the one Microsoft corrected on October 20: Mitigated.
The durable point
Vendor status pages are claims, not proof. Resolved is a word a vendor types; working is a thing your pilot ring demonstrates. The boring habit that survives weeks like this one is simple. Test the fix on a few machines, watch the behaviour that actually broke, and only then change the fleet and close the paperwork. Microsoft will ship the real fix in the coming weeks. Your workaround, applied once and left alone, is what keeps people connected until it does.
Sources
- "Microsoft admits that Always On VPN problems were not fixed in the October Security Update" — The Register, October 20, 2026
- "Microsoft fixes VPN issues caused by September Windows updates" — BleepingComputer, October 2026